The preview endpoint runs custom code inside a sandbox. The registration endpoint compiles the same code directly in the application process.
The sandbox may be working exactly as designed. The system still has an uncontained execution path.
This is an illustrative architecture to investigate, not a claim about a particular deployment. It captures the review problem highlighted by the LiteLLM guardrail research: related features can reach code execution through different validation and runtime paths.
Search for every entrance
Start with features that can load a package, import a module, compile a template, run a callback, or launch a process.
Include installation, registration, preview, testing, migration, background tasks, and startup. Security reviews often concentrate on the path users click most often. Attackers can choose a different one.
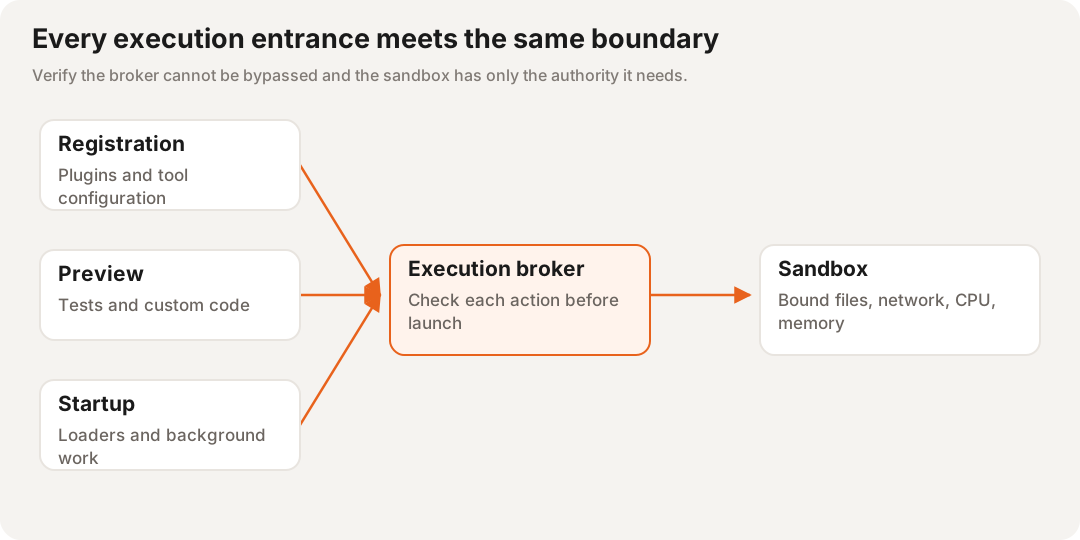
Each execution request crosses the broker. A shared broker is useful only when alternate paths cannot bypass it.
Compare the paths
| Entry point | Identity and permission | Executor | Files, credentials, and network |
|---|---|---|---|
| Preview | Who may submit this code? | Which process runs it? | What can that process reach? |
| Registration | Who may install or replace it? | Does registration execute anything? | Does it inherit application secrets? |
| Startup | Which approved artifact loads? | Does initialization use the broker? | Are mounts and egress equally narrow? |
Fill this in with effective runtime behavior. A function named safe_execute tells the reviewer little about the process, account, mounts, or resource limits it actually uses.
Ask two different questions
First, can an execution path avoid confinement? Centralize policy checks and process creation so registration or background work cannot create an alternate executor.
Second, if arbitrary code runs inside the sandbox, what can it do? Review filesystem mounts, host sockets, cloud credentials, network access, CPU, memory, and tenant state.
Blocking a few language built-ins is insufficient when imports, native extensions, subprocesses, or reflection remain available.
Test a harmless boundary crossing
Use controlled canary files and endpoints. Submit the same test operation through every entry point. Confirm both the broker decision and the operating-system outcome.
Also exercise timeouts and cancellation. A worker left running after rejection can outlive the policy decision that was supposed to stop it.
Keep the evidence tied to the deployed configuration. The strongest assurance comes from showing that each path enters confinement and that the confined process has only the authority its task requires.